
A vendor building your patient portal can end up handling protected health information long before launch, in test data, integrations and support tickets. Healthcare software outsourcing hands over the code, but it doesn't hand off the paperwork: HIPAA still expects a written contract with anyone who handles patient information on your behalf.
Our view is simple. Outsource the build when you lack a team with compliance experience, keep product decisions with your own people, and treat the contract as part of the project rather than a formality at the end.
What healthcare software outsourcing gets you
The main gain is access to a team that has already worked on the terrain. A healthcare product needs authentication, audit trails, integrations with clinical systems and a clear answer on data retention, and an outside team that has built these before spares you paying for a new hire to learn them.
Capacity is the second gain. A launch needs designers, engineers and testers for a stretch and far fewer afterwards, so an outside team lets the headcount follow the workload instead of leaving idle salaries behind.
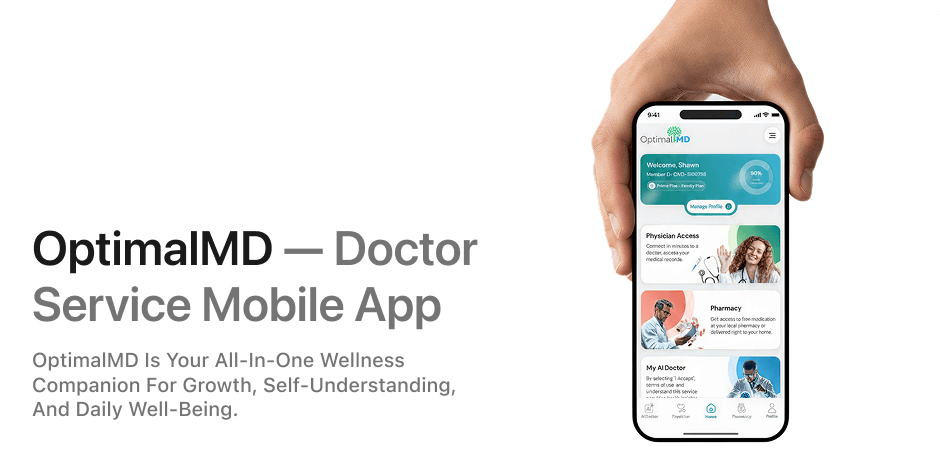
When we designed and built OptimalMD's website, members portal and mobile app end to end, a single team carried the product from design through launch.
Where the risks sit
Distance is the first one. Healthcare Compliance Pros, a compliance advisory firm, writes that OCR's enforcement against offshore vendors is "limited at best" and that business associate agreements offer "limited protection" for organisations using offshore services. If your vendor is overseas, you can't count on a regulator to do the chasing for you.
So the protection has to come from what you check before signing and what you watch afterwards. The same firm recommends encryption, access controls, regular security audits, staff training and a risk assessment before the engagement starts.
Then there's the chain you never see. Under the federal rule, a business associate must make its subcontractors agree to the same restrictions and conditions that apply to it. Ask the vendor who else will touch your data, whether that's freelancers, hosting or support tooling, before the contract is signed, because every name on that list needs the same terms.
Requirements lost in handover are the quieter risk. A named product owner on your side and a demo on a fixed cadence catch most of it early.
What the contract has to say before work starts
The business associate contract must set out how the vendor may use and disclose protected health information, and it can't authorise uses you couldn't make yourself. It must also require appropriate safeguards against any use the contract doesn't allow.
Those are the minimum terms the rule asks for. Offshore arrangements deserve more: Healthcare Compliance Pros also points to confidentiality agreements and mechanisms for monitoring and overseeing the provider, which in practice means audit rights and a named person who reviews access.
For a build that includes compliance-heavy work, our write-up on what HIPAA compliant app development actually takes covers the engineering side that the contract can't.
Deciding what to outsource and what to keep
Photo by Vitaly Gariev on Pexels
Outsource the work that has a clear definition of done: the portal, the mobile app, the integrations. Keep ownership of the product roadmap, the patient data decisions and the relationship with your clinical staff.
Start small if the scope is unclear. Pricing a first release before committing to a full platform is what our guide to healthcare startup MVP cost walks through, and the broader healthcare software development guide shows what a full build involves. If you'd like a team to scope it with you, that's the work our apps and SaaS service covers.
Before you sign anything, ask the vendor for the list of everyone who will touch your data and for the exit terms in writing.
Frequently asked questions
What should the vendor do if patient data is exposed?
The contract must require the vendor to report to you any use or disclosure of the information that the contract doesn't provide for. That includes breaches of unsecured protected health information.
What happens to our data when the contract ends?
At termination the vendor must return or destroy all protected health information if that's feasible, and keep no copies. If it isn't feasible, the contract's protections continue to apply to whatever is kept.
Can we end the contract if the vendor breaks the terms?
Yes. The rule requires the contract to let you terminate it if you determine the vendor has violated a material term.
Cover photo by Daniil Komov on Pexels
Sources
- 45 CFR 164.504 - Uses and disclosures: Organizational requirements — Cornell Law School Legal Information Institute
- How to Utilize Offshore Vendors without Breaking the Law — Healthcare Compliance Pros